> For the complete documentation index, see [llms.txt](https://book.redsquad.xyz/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://book.redsquad.xyz/web-hacking/sessions-tokens/cookies.md).
# Cookies
{% hint style="info" %}
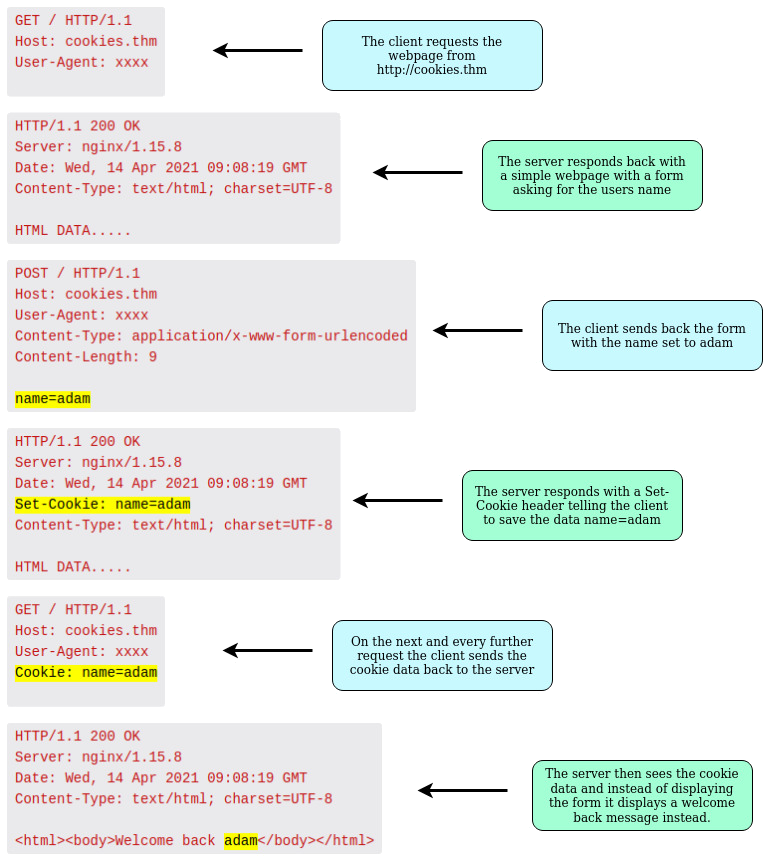
Cookies are small bits of data that are stored in your browser. **Each browser will store them separately, so cookies in Chrome won't be available in Firefox.** They have a huge number of uses, but the most common are either session management or advertising (tracking cookies). Cookies are normally sent with every HTTP request made to a server.
You can check your cookies security attributes with **ZAP** or **Nikto**.
{% endhint %}
## Brief
### Define Cookies attributes
{% embed url="" %}
Testing for cookies attributes - OWASP
{% endembed %}
#### Restrict access to cookies
* **Secure**
* Only sent to the server with an encrypted request over HTTPS, never sent with HTTP.
* **HTTPOnly**
* Inacessible to Javascript document.cookie API; only sent to the server, helps mitigate XSS attacks.
* **Path**
* Limits the scope of a cookie to a specific path on the server and can therefore be used to prevent unauthorized access to it from other applications on the same host.
#### Define where cookies are sent
* **SameSite**
* The SameSite attribute lets servers specify whether/when cookies are sent with cross-site requests (where Site is defined by the registrable domain). This provides some protection against cross-site request forgery attacks (CSRF).
* It takes three possible values: **Strict**, **Lax**, and **None**.
### Cookies prefixes
{% embed url="" %}
Define where cookies are sent
{% endembed %}